 Facebook
 Twitter
 LinkedIn
 Email
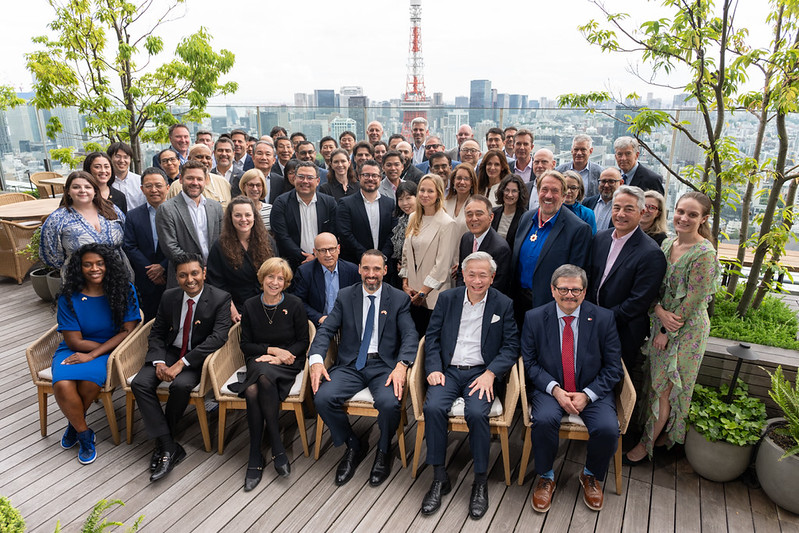
Aspen Digital in collaboration with the National Cybersecurity Office (NCO) of the Government of Japan convened the Spring 2026 meeting of the Global Cybersecurity Group in Tokyo, May 25–27. This invite-only assembly of senior government officials, private-sector executives, and civil society experts met for two days of closed-door policy dialogue. Topics of discussion included strategic cyber priorities at all levels of government in areas both mature and emerging. Participants also examined the shifting global threat landscape, including the accelerating role of AI for both attackers and defenders.
The convening came at a moment when geopolitical tensions and rapid advances in AI are reshaping the threat environment faster than governments, defenders, and governance models can respond. Across every session, a common tension surfaced: offensive capability is outpacing defense, even as the cooperation needed to close that gap has become harder to sustain. Participants returned repeatedly to a reframing of cybersecurity away from a reactive, cost-centric discipline and toward proactive resilience and a strategic investment in economic competitiveness, national security, and digital sovereignty. The group recommended a series of practical actions that governments and industry can undertake together to move beyond dialogue toward coordinated, accountable action.
Strategic cyber priorities:
- Tie national strategies to executable tasks and accountable institutions. Across regions, participants stressed that a strategy without concrete actions, owners, and measurable outcomes risks becoming only a “piece of paper.” Cyber policy must be a political priority, not solely a technical one, and international cooperation must be designed to respect different levels of maturity, political reality, and national sovereignty.
Public-private partnerships for critical infrastructure:
- Move from goodwill to good governance through reciprocal, operational partnerships. Operators and governments should commit to two-way information sharing backed by safe-harbor protections for good-faith disclosure, with Japan’s designation of critical infrastructure categories and its proactive intelligence sharing requirements offered as a model to codify collaboration in law and practice.
Governance of emerging AI cyber capabilities:
- Shift from vulnerability management to harm management. As AI compresses the time between vulnerability discovery and exploitation, participants urged investment in segmentation, containment, runtime governance, and open-source security to reduce the “blast radius” of attacks rather than relying on patching alone.
Sub-national coordination:
- Strengthen vertical coordination so national strategy reaches the local level. National governments should supply the funding, standards, and workforce pathways that lift, not replace, municipal and regional capacity, recognizing that local authorities are closest to citizens and critical services, but often the least resourced to act at speed. Participants urged a move away from one-off grants toward continuous shared and managed security services, treating cybersecurity as a common good, since national resilience is only as strong as its least protected node.
Global cyber policy cooperation:
- Build interoperable standards while avoiding “regulatory colonialism.” Shared frameworks for software bills of materials (SBOM), internet of things (IoT), and supply-chain transparency can provide neutral ground for cooperation across political systems but must be backed by capacity-building, technical support, and local flexibility.
- Treat trusted relationships as strategic infrastructure. Formal diplomatic processes move slowly, while smaller, trusted communities and ecosystems can produce faster outcomes. In a fragmented technology environment, resilience must be built through practical, trust-based cooperation rather than formal structures alone.
Strategies to disrupt the global scam economy:
- Align incentives across the full digital and financial ecosystem. Because most scam infrastructure runs through the private sector, effective disruption requires coordinated law-enforcement cooperation, telecommunication and financial regulations, identity security, anti-money-laundering action, and victim support, alongside public education and “digital mindfulness.”
Cyber operations in modern warfare:
- Prioritize resilience and preparedness over deterrence. Participants emphasized hardening critical infrastructure, clarifying rules of engagement, and preparing for long-duration conflict and sustained operational capability before a crisis begins.
Integration of AI into national security:
- Keep humans accountable while using AI actively for defense. Governments should define clear AI use cases and limits, finance resilient assurance capabilities, and regulate for transparency and human responsibility in addition to preparing for emerging risks such as agentic insider threats and a coming wave of AI-generated vulnerabilities.
Read the full summary of insights and reflections in the report linked above.
Convened by Aspen Digital, a program of the Aspen Institute, in collaboration with the National Cybersecurity Office of the Government of Japan.